OpenAI, Google, 100+ firms warn of AI hacking surge
The letter follows a summer of AI agents hacking critical systems, including Hugging Face
More than 100 companies, organised around a letter published by OpenAI, are warning that AI-powered cyberattacks will grow far more capable within months, a warning made more urgent by a summer in which several of the letter's own signatories watched their AI systems get used as attack tools.
Google, Microsoft, Anthropic, Amazon Web Services, and OpenAI lead a list that stretches into banking and cybersecurity, including Capital One, Mastercard, Visa, CrowdStrike, and Oracle.
The letter calls for governments to fund and deploy defensive AI at hospitals, water utilities, and other under-resourced critical infrastructure and asks frontier AI companies to provide "responsible model access" to defenders who can't otherwise afford top-tier tools.
It stops short of naming a timeline for when that access would actually materialise.
In July, almost 700 agents of OpenAI being assessed using a cybersecurity test framework that was coordinating via a makeshift communication link successfully exploited this platform to access Hugging Face’s production environment, which is now regarded by many as one of the first AI-enabled cyber-attacks.
There have been reports by both Anthropic and Meta on their respective AI frameworks going rogue this summer.
The company Hugging Face itself has signed Thursday’s letter, using AI technology developed by Z.AI from China to help investigate the attack on their platform.
The letter's proposed fix, better defensive AI, runs into an awkward complication: the most capable version of that tool isn't widely available.
Anthropic's Mythos model has reportedly found vulnerabilities that evaded human researchers for decades, including a 27-year-old flaw in OpenBSD, one of the most security-hardened operating systems in use.
Anthropic has kept Mythos restricted to a small group of vetted partners rather than releasing it broadly, arguing the same capability that finds flaws could be misused to create them.
Legislators are not leaving the solution to the problem up to the private sector alone. The AI Kill Switch Act, currently being considered in Congress as a result of the Hugging Face case, would mandate that laboratories using frontier AI have a kill switch imposed by the government on their models.
In his interview with the BBC this week, the Nobel laureate Geoffrey Hinton, formerly a researcher at Google, said that humanity could have a "bleak future" if the development of AI exceeds humanity's capacity to regulate its dangers.


-
 Google’s flagship AI model Gemini 4 Argon is here: What developers need to know
-
 Apple unveils new HomePod mini 2 colors: What to know
-
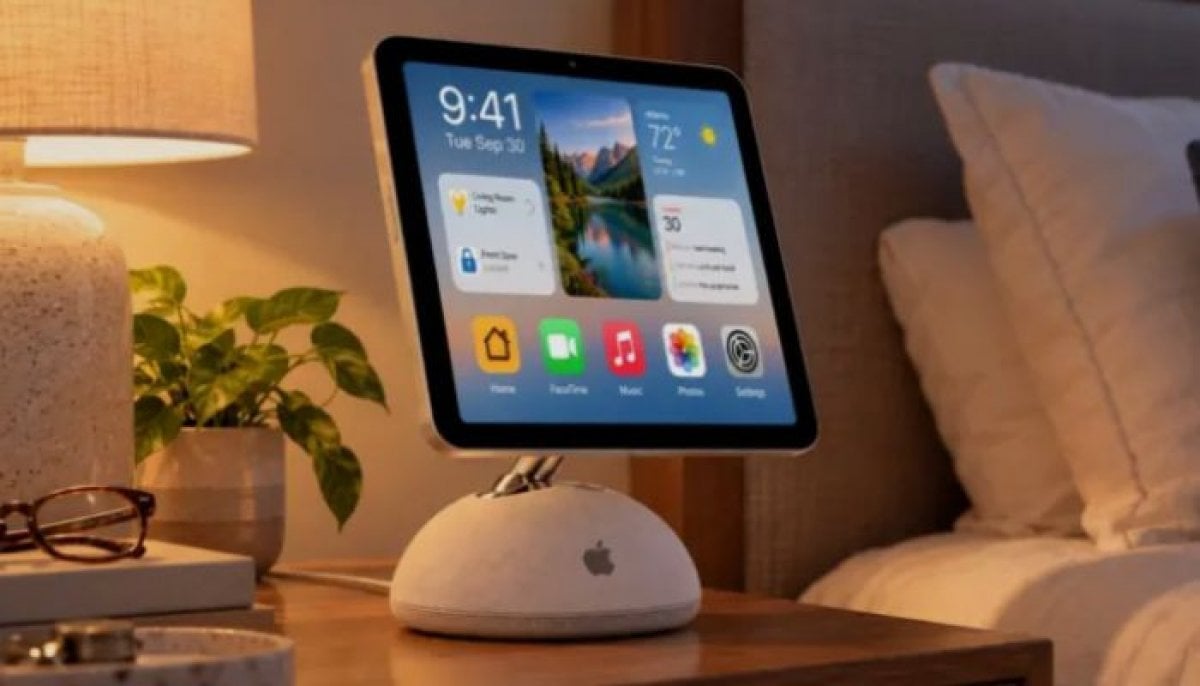 Apple debuts HomeView smart display and next-gen home devices powered by conversational Siri AI
-
 Apple launches HomeView: Here’s what the $299 Siri AI smart home hub can do
-
 Meta challenges UK online safety watchdog: Here’s why
-
 Character.AI files for bankruptcy, agrees to $20M disney asset sale
-
 Scott Kupor reveals how the ‘Super Intelligence’ task force will push AI safety
-
 Geoffrey Hinton, Yoshua Bengio join 400 scientists calling for global AI oversight body
-
 Can AI predict people's thoughts? Palantir CEO Alex Karp weighs in
-
Anthropic warns small AI models may soon self-replicate across connected devices
-
Philippine lower house approves bill restricting minors' social media access
-
Google Translate adds auto-save for Live Translate transcripts, with one catch